LIVE
Battleground
Competitive jeopardy and attack-defense challenges across web, crypto, pwn, forensics, reversing, and OSINT — live leaderboards, seasonal events, solo and team play.
RankTeamScore
OFFENSIVE SECURITY · DEFENSIVE OPERATIONS · CYBER RANGES
Air Realm is the offense–defense proving ground for the next generation of security teams — VAPT, SOC-as-a-Service, OT Security, and Research & Innovation delivered alongside live Red vs Blue ranges and a competitive Battleground, all engineered for the AI era.
● LIVE NOW
Four live platforms individuals and teams compete and train in directly — one part of everything Air Realm runs. Our full service portfolio, from VAPT to OT Security, is below.
Competitive jeopardy and attack-defense challenges across web, crypto, pwn, forensics, reversing, and OSINT — live leaderboards, seasonal events, solo and team play.
Offensive simulation infrastructure for adversary emulation — build attack chains, pivot through networks, and test exploit development in isolated ranges.
Defensive ranges wired with real SIEM and EDR telemetry — triage alerts, hunt threats, and run incident response against live, planted attack data.
Always-on hands-on labs — live VMs, real networks, and a growing set of challenges anyone from complete beginners to working professionals can jump into anytime.
● ENTERPRISE TOOLING
Every range runs on the same industry-standard tooling production security teams rely on — not cut-down simulators.
 Splunk
 Wazuh
 Velociraptor
 Wireshark
 TheHive
 MISP
 Metasploit
 Nmap
 Kali Linux
 Burp Suite
 Elastic SIEM
 MITRE ATT&CK
● OUR SERVICES
All active today — delivered by the same operators who build and run our live ranges, not a separate bench of consultants.
Vulnerability assessment & penetration testing across web, mobile, network, cloud and API attack surfaces — manual testing backed by proof-of-exploit reporting.
Learn More →24/7 managed detection & response — log monitoring, threat hunting, and incident response delivered by analysts trained inside our own Blue Team range.
Learn More →Video lectures and hands-on practice challenges for SOC analysts and red teamers — separate from live competition, built for steady skill-building at your own pace.
Learn More →Security assessment and monitoring for operational technology and industrial control systems — built around the safety and uptime constraints IT-style testing ignores.
Learn More →How we collaborate — original research, tool development, and partnerships with academia and industry that feed directly back into every range and service we run.
Learn More →WHY AIR REALM
Red and Blue live in the same ecosystem, so every attack we build makes our detections sharper — and every detection we tune makes our attacks harder to spot.
Real SIEM, real EDR, real attack infrastructure — not toy sandboxes. What you practice on is what production security teams actually run.
Scenarios are built for the threats and tooling of now — AI-assisted attacks, AI-assisted detection, and the analysts who have to keep up with both.
No support ticket queue. Direct access to the team designing the ranges, the services, and the roadmap.
New scenarios, new challenges, new attack paths — the Realm is a living environment, not a static course.
Compete, defend, attack, and train in a single connected platform instead of stitching together five different tools.
ROADMAP
Battleground, Red Realm, Blue Realm, and Onyx, plus VAPT, SOC-as-a-Service, Training Platform, OT Security, and Research & Innovation — all live today.
A live, safe-to-break ICS/SCADA range environment, built on the same infrastructure as our IT-focused ranges.
Assessed certification paths built on top of the Training Platform's existing lecture and hands-on lab content.
Growing our academic and industry collaborations under Research & Innovation into a standing, published research program.
FROM THE REALM
Alert fatigue is a design problem, not a staffing problem. Here's how we tune our SOC-as-a-Service to avoid it.
Attackers are already using AI to move faster. Detection has to catch up — here's how we're building for it.
The single biggest mistake we see in industrial environments: treating OT security like IT security.
Alert fatigue is a design problem, not a staffing problem. Here's how we tune our SOC-as-a-Service to avoid it.
Attackers are already using AI to move faster. Detection has to catch up — here's how we're building for it.
The single biggest mistake we see in industrial environments: treating OT security like IT security.
● LIVE FEED
Real-time headlines aggregated from trusted security industry sources.
Japanese manufacturer Iris Ohyama, the operator of the Iris Plaza shopping platform, disclosed that personal information belonging to about 7.7 million people may have been exposed after unauthorized access to a third-party cloud service the company used. [...]

Its multi-agent AI platform generates the telemetry an attack would produce to fix gaps in enterprise defenses. The post Brava Security Emerges From Stealth With $15 Million in Funding appeared first on SecurityWeek.
French cooperative bank Crédit Mutuel Arkéa was targeted in a cyberattack that enabled fraudulent transactions of up to $133 million, forcing it to respond by suspending certain systems.v [...]
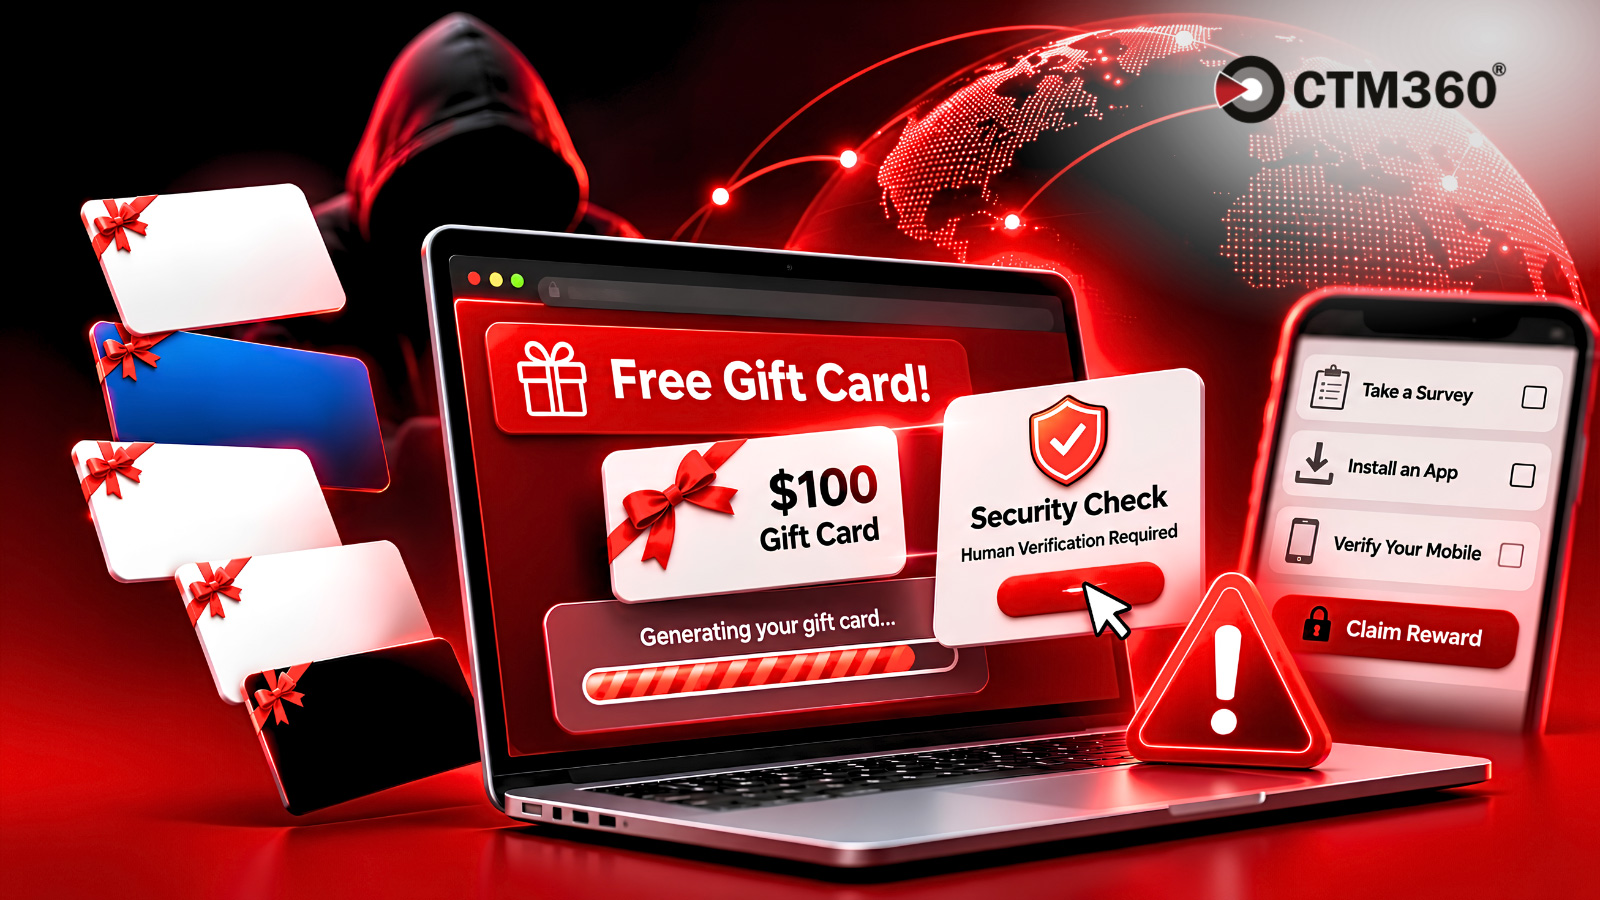
Scammers are impersonating major brands and celebrities to lure consumers into fake gift card giveaways that collect personal information and trigger unwanted subscriptions. CTM360 reveals how these campaigns use deceptive verification steps and affiliate networks to generate revenue without delivering the promised rewards. [...]
Japanese manufacturer Iris Ohyama, the operator of the Iris Plaza shopping platform, disclosed that personal information belonging to about 7.7 million people may have been exposed after unauthorized access to a third-party cloud service the company used. [...]
Its multi-agent AI platform generates the telemetry an attack would produce to fix gaps in enterprise defenses. The post Brava Security Emerges From Stealth With $15 Million in Funding appeared first on SecurityWeek.
French cooperative bank Crédit Mutuel Arkéa was targeted in a cyberattack that enabled fraudulent transactions of up to $133 million, forcing it to respond by suspending certain systems.v [...]
Scammers are impersonating major brands and celebrities to lure consumers into fake gift card giveaways that collect personal information and trigger unwanted subscriptions. CTM360 reveals how these campaigns use deceptive verification steps and affiliate networks to generate revenue without delivering the promised rewards. [...]
GET IN TOUCH
Whether you want early access to the Realm, a VAPT briefing, or just want to say hello — reach out.